Cybersecurity & Compliance Strategy for a Wealth Management Firm
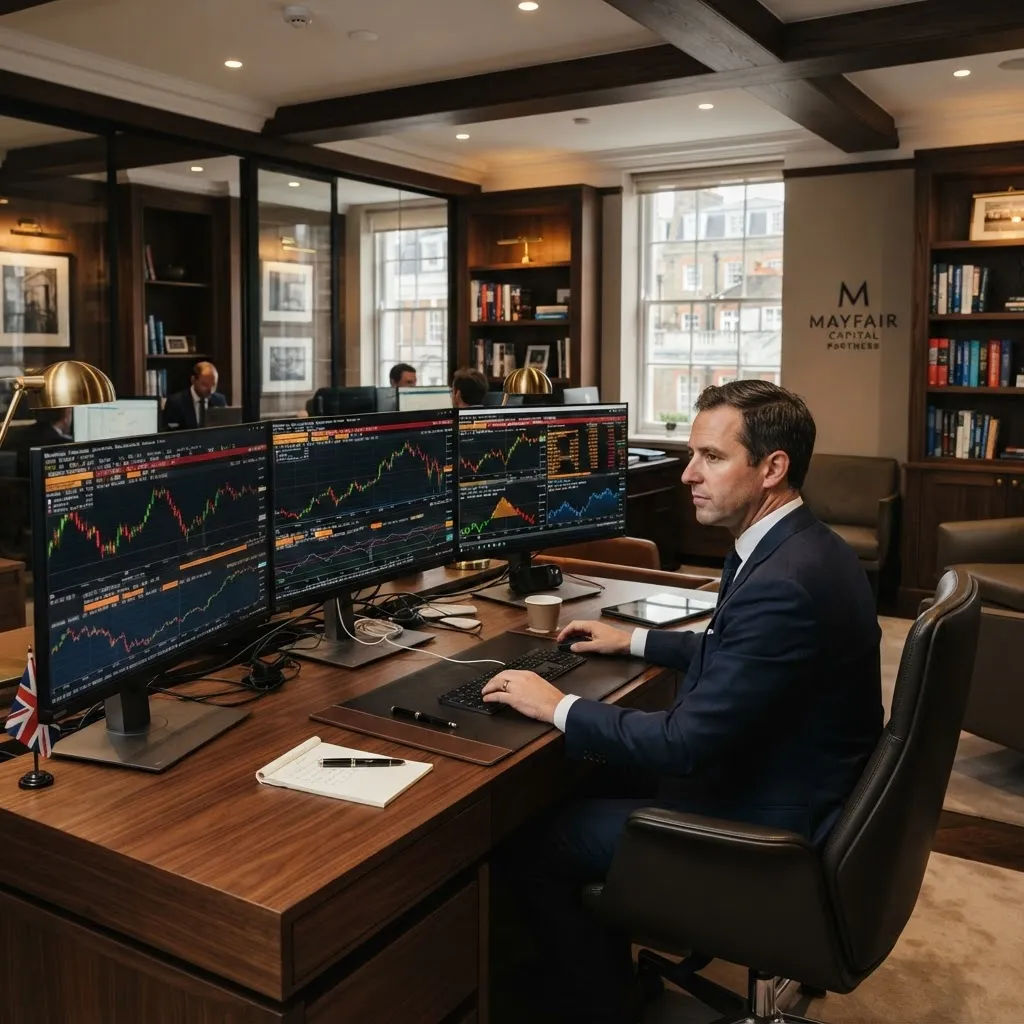
99.97% of malicious email blocked before reaching users. We delivered this outcome for Mayfair Wealth Management Firm (45 users) by combining Mimecast, Exchange, Office 365 into a single strategic engagement.
What Mayfair Wealth Management Firm was facing
A Mayfair-based wealth management firm was experiencing an increasing volume of phishing emails, including targeted business email compromise attacks. Their existing email security was not catching sophisticated impersonation attempts, and they needed strategic guidance to meet FCA compliance requirements for email retention and legal hold. They lacked a cybersecurity roadmap and needed an advisor to assess their risk posture and design a comprehensive defence strategy.
How we solved it
We began with a cybersecurity risk assessment and gap analysis, then delivered a multi-layered defence strategy with Mimecast as the email security foundation. We designed impersonation protection rules, continuity services, and a 10-year compliance archive for FCA requirements. We also created a security awareness training programme with monthly phishing simulations. Throughout, we advised the firm's leadership on regulatory compliance, risk mitigation, and ongoing security posture management.
What we delivered
The Threat: Sophisticated Phishing Targeting a Wealth Management Firm
A Mayfair-based wealth management firm with 45 users was experiencing an increasing volume of sophisticated phishing emails, including targeted business email compromise (BEC) attacks. The attacks were not random — they were carefully crafted to impersonate the firm's senior partners, using lookalike domains, spoofed email headers, and social engineering techniques designed to trick staff into changing client bank details or authorising fraudulent transfers. The firm's existing email security (Office 365's built-in protection) was not catching these targeted attacks.
The firm had experienced three near-miss incidents in six months. In the first, a client received an email that appeared to be from their wealth manager requesting a change to their bank details — the client called the firm to verify, and the fraud was detected. In the second, a staff member received an email that appeared to be from the managing partner requesting an urgent wire transfer — the staff member noticed a slight difference in the email address and reported it. In the third, a partner's email account was compromised, and the attacker sent phishing emails to the partner's clients from the compromised account. The firm was lucky — but they knew their luck would run out.
The firm also needed to meet FCA compliance requirements for email retention and legal hold. Financial services firms are required to retain all email communications for a minimum of 5 years, with the ability to place legal holds on specific mailboxes to prevent deletion during investigations. The firm had no email archiving solution — they were relying on Exchange Online's built-in retention, which was not sufficient for FCA compliance and did not provide the tamper-proof archiving that regulators required.
The Assessment: Cybersecurity Risk and Gap Analysis
We began with a comprehensive cybersecurity risk assessment and gap analysis. We reviewed the firm's email security configuration, analysed the phishing emails that had bypassed existing protections, and assessed the firm's compliance posture against FCA requirements. The assessment identified four critical gaps: insufficient email security (no advanced threat protection, no impersonation protection, no email continuity), no compliance archiving (no tamper-proof email retention, no legal hold capability), no security awareness training (staff were not trained to recognise sophisticated phishing), and no incident response plan (no documented procedure for responding to email security incidents).
We recommended Mimecast as the email security and archiving platform. Mimecast provided four layers of protection that addressed all the gaps: threat detection (blocking phishing, malware, and impersonation), email continuity (maintaining email access during outages), compliance archiving (tamper-proof 10-year archive with legal hold), and security awareness training (phishing simulations and training modules). The firm's partners approved the recommendation, and we began the implementation.
Implementation: Impersonation Protection and Compliance Archiving
The implementation was completed in 2 weeks. Week 1 was the Mimecast deployment. We configured Mimecast as the email gateway, routing all inbound email through Mimecast before it reached Microsoft 365. We configured impersonation protection rules tailored to the firm's senior partners — Mimecast would flag any email that mimicked a partner's name, used a lookalike domain, or displayed unusual sending patterns. We also configured Safe Links (real-time URL scanning that rewrote links in emails and checked them at click time) and Safe Attachments (sandbox detonation of email attachments to detect zero-day malware).
We also configured email continuity. Mimecast's continuity service meant that if Microsoft 365 experienced an outage, the firm's staff could continue sending and receiving email through Mimecast's web-based interface — with all email synced back to Microsoft 365 when the outage was resolved. This was critical for a wealth management firm where email communication with clients was time-sensitive and any outage could result in missed investment opportunities or delayed transactions.
Week 2 was the compliance archiving configuration. We configured Mimecast's archiving service to capture every email sent and received by the firm, storing it in a tamper-proof archive for 10 years. The archive was write-once-read-many (WORM), meaning emails could not be deleted or modified — even by an administrator. We configured legal hold policies that allowed the firm's compliance officer to place holds on specific mailboxes, preventing any deletion during investigations. And we configured the archive to support FCA compliance reporting, with the ability to search, export, and produce email records on demand.
Security Awareness Training: Building a Human Firewall
Technology alone could not stop all phishing attacks — the firm's staff were the last line of defence, and they needed to be trained to recognise and report sophisticated phishing attempts. We deployed Mimecast's security awareness training programme, which combined monthly phishing simulations with targeted training modules for users who clicked.
The first phishing simulation, sent 2 weeks after the Mimecast deployment, had a 23% click rate — nearly a quarter of staff clicked on a simulated phishing email. This was a wake-up call for the firm's partners, who had assumed that their sophisticated staff would be immune to phishing. We immediately enrolled all staff in Mimecast's training modules, covering phishing recognition, business email compromise, safe browsing habits, and reporting procedures.
Over the following 6 months, the click rate dropped steadily: 23% → 15% → 9% → 6% → 4%. Each month, users who clicked on the simulation received instant, targeted training — a 5-minute module that explained the specific phishing technique they had fallen for and how to recognise it in the future. The training was not punitive — it was educational, designed to build a culture of security awareness rather than fear of making mistakes.
We also implemented a simple reporting mechanism: a 'Report Phishing' button in Outlook that allowed staff to report suspicious emails with one click. Reported emails were analysed by Mimecast and, if confirmed as phishing, added to the threat intelligence database — improving protection for all Mimecast customers. In the 12 months following the training programme, staff reported 47 suspicious emails, of which 12 were confirmed as phishing attempts that had bypassed Mimecast's automated detection — proving that the human firewall was a valuable complement to the technical controls.
Outcome: 99.97% of Malicious Email Blocked, FCA Compliance Achieved
In the 12 months following the Mimecast deployment, 99.97% of malicious email was blocked before reaching users — including all impersonation attempts targeting the firm's senior partners. Zero successful phishing incidents occurred, compared to three near-misses in the 6 months before deployment. The phishing simulation click rate dropped from 23% to 4%, and staff reported 47 suspicious emails — demonstrating that the security awareness training had transformed the firm's human firewall.
FCA email retention compliance was achieved with the 10-year tamper-proof archive. The firm's compliance officer could search, export, and produce email records on demand, and legal hold could be applied to any mailbox with a single click. When the FCA conducted a routine compliance review 4 months after the deployment, the firm's email archiving was cited as 'best practice' — the first time the firm had received such a commendation.
Email continuity was tested during a Microsoft 365 outage that lasted 3 hours. The firm's staff continued sending and receiving email through Mimecast's web interface, and all email was synced back to Microsoft 365 when the outage was resolved. The firm's clients noticed nothing — their emails were answered on time, and no investment opportunities were missed. The managing partner described the continuity service as 'insurance that actually paid out — we didn't lose a single client communication during the outage.'
Tools and skills applied
Get results like these for your business
Tell us about your project and a certified consultant will call you back within 10 minutes. No obligation, no pressure.
Questions about this case study
Common questions about the project, timeline, and results.
Related services & insights
The financial services expertise and technical capabilities behind this engagement.
Services

Email Security (Mimecast)
Enterprise-grade email security with Mimecast to stop phishing, ransomware, and business email compromise.
Cyber Security Services
Managed cyber security services protecting UK businesses from evolving threats — risk assessments, defence-in-depth, compliance, and 24/7 monitoring.
Microsoft 365 Support
Microsoft 365 support services — expert setup, zero-downtime migration, security hardening, and ongoing management of your productivity suite.
Tech Insights

Ransomware Protection: A Complete Defence Strategy for UK Businesses
Ransomware attacks cost UK businesses £1.2 billion in 2025. Here's the seven-layer defence strategy we deploy for clients — from immutable backups to employee training — that stops attacks before they encrypt.
Active Directory Security: A Hardening Guide for UK IT Admins
Active Directory is the keys to your kingdom — and the #1 target for attackers. Here are the 12 security controls every UK business should implement to protect their identity infrastructure.

Microsoft 365 Migration: A Step-by-Step Guide for SMEs
Migrating to Microsoft 365 without downtime or data loss. The exact phased approach our engineers follow, from audit to go-live.
Sources & further reading
Independent guidance from UK regulators, standards bodies and technology vendors that underpins the advice on this page.
- National Cyber Security CentrePhishing: how to spot and report scamsHow to recognise, report and harden against email-borne attacks.(opens in a new tab)
- MimecastEmail security and resiliencePlatform documentation for the email security service we deploy.(opens in a new tab)
- MicrosoftSecurity threat intelligence and researchVendor threat research and product security guidance.(opens in a new tab)
- National Cyber Security Centre10 Steps to Cyber SecurityThe UK's baseline framework for protecting business systems, people and data.(opens in a new tab)
Book your free consultation
in 30 seconds.
No obligation. No spam. Just a certified engineer with a clear, proactive roadmap.